TRUST CENTER
How we protect your data and your patients' data: what we commit to, what we are certified for, and what we don't claim.
Last reviewed:

Healthcare and HIPAA
Woltrio builds software for healthcare organizations as a HIPAA business associate. These are the commitments we make in every healthcare engagement.
BAA before any PHI
We sign our standard Business Associate Agreement before any protected health information (PHI) is shared. You can review it before you sign a contract.
PHI stays in your AWS account
Healthcare products are deployed in your own AWS account, under your BAA with AWS. Woltrio does not store or process PHI on its own systems.
Synthetic data for development
We build and test with dummy data only. Our engineers do not work with real patient records.
Access is limited and logged
When we need access to your environment, you grant it to named accounts with only the permissions the work needs. Every action is recorded in audit logs in your account, and our access is removed at handover.
Breach notice within 3 business days
If we discover an incident affecting your PHI, we notify you within 3 business days, well inside HIPAA's 60-day limit. We then contain it, investigate, and send you a written report.
Annual HIPAA training
Every member of staff completes HIPAA training each year.
Annual risk assessment
We assess threats to PHI and to our systems at least once a year, and whenever we take on a new system or PHI workflow, under the risk methodology of our ISO/IEC 27001 management system.
Who is responsible for what
Our default split on healthcare projects. Anything different for your project is agreed in writing in the contract and BAA.
| Area | You | Woltrio |
|---|---|---|
| AWS account and AWS BAA | You own the AWS account and sign AWS's BAA. | We work inside your account through access you grant. |
| Where PHI is stored | Only in your AWS account. | Never on our systems. We build and test with synthetic data. |
| Encryption keys | Held in AWS KMS in your account. | We set up encryption and use keys only through access you grant. We keep no copies. |
| Backups | Stored in your AWS account. | We configure and test them during the project. |
| Audit logs | Kept in your account, under your retention policy. | Every action we take in your environment is logged there. |
| Production access | You grant and revoke named accounts. | Least privilege only. Our access is removed, and confirmed in writing, at handover. |
| Incident response | You lead the response and the notifications HIPAA requires. | We notify you within 3 business days of anything we find, help contain and investigate it, and send a written report. |
Independent assurance: what we have and what we don't
Documents available under NDA
Sent once a mutual NDA is signed.
- Sample Business Associate Agreement
- Statement of Applicability (ISO/IEC 27001)
- Information Security Incident Response Procedure
- PHI Handling & Privacy Policy
- Risk Assessment Methodology
- Business Continuity & Disaster Recovery Procedure
ISO/IEC 27001:2022 certificate
The information security management system (ISMS) at Woltrio's development center in Rawalpindi, Pakistan, is independently certified by G-CERTI, an IAS-accredited certification body. That is where our engineering team designs, builds and deploys client software. Every detail below comes from the certificate itself.
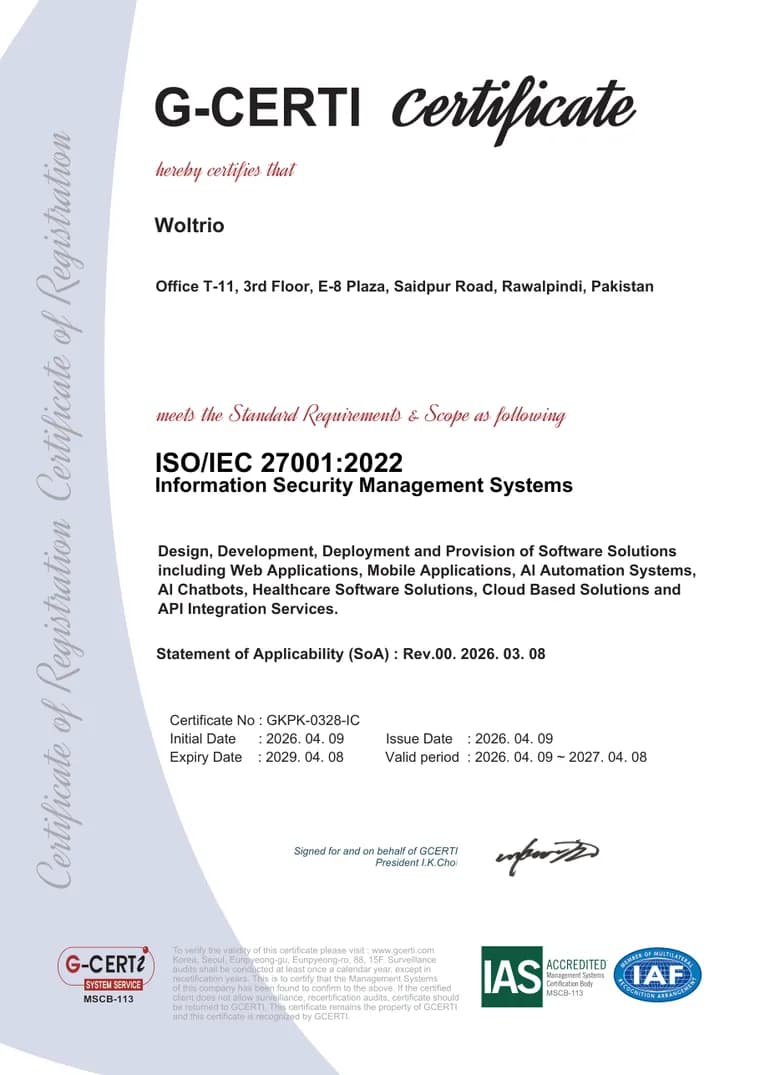
Independently verifiable on IAF CertSearch, the International Accreditation Forum's global certificate database (certificate no. GKPK-0328-IC).
- Standard
- ISO/IEC 27001:2022
- Certificate no.
- GKPK-0328-IC
- Certification body
- G-CERTI
- Accreditation
- IAS (MSCB-113) · IAF MLA
- Scope
- Design, Development, Deployment and Provision of Software Solutions including Web Applications, Mobile Applications, AI Automation Systems, AI Chatbots, Healthcare Software Solutions, Cloud Based Solutions and API Integration Services.Scope as worded on the certificate. It covers the ISMS at our Rawalpindi development center — the way we design, build, deploy and support software — not individual client products.
- Certified site
- Office T-11, 3rd Floor, E-8 Plaza, Saidpur Road, Rawalpindi, PakistanOur headquarters in Denver, Colorado (Woltrio LLC) is outside the certificate's scope.
- First certified
- Current validity until
- Kept in force by an annual surveillance audit; the certificate is reissued after each one.
- Certification cycle ends
- Statement of Applicability
- Rev.00 (2026-03-08)
PSEB registration
Woltrio is a registered software company with the Pakistan Software Export Board (PSEB), the government body under the Ministry of IT & Telecom that registers and oversees Pakistan's software and IT services exporters.
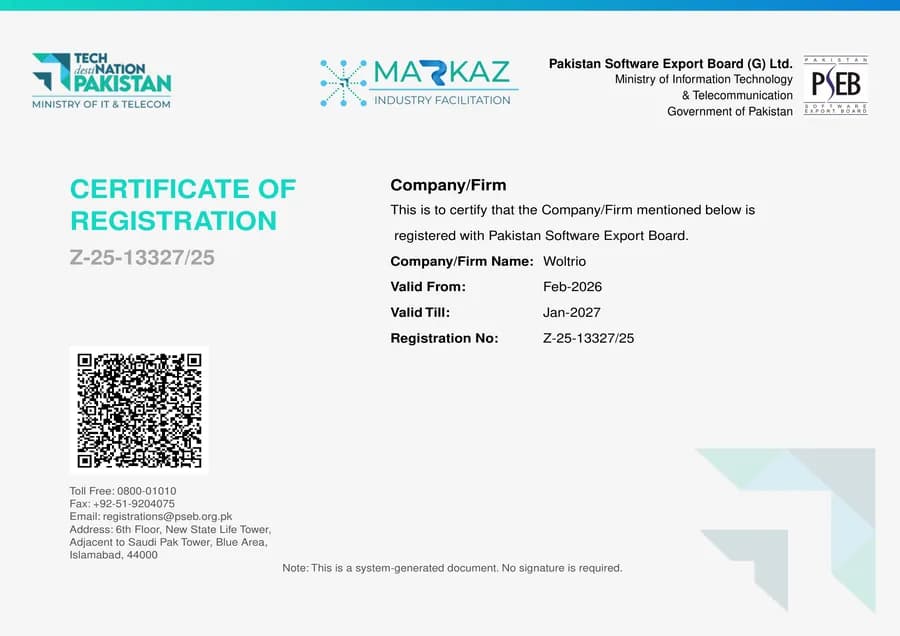
Opens PSEB's official verification page for registration no. Z-25-13327/25 — the same link as the QR code on the certificate.
- Registration no.
- Z-25-13327/25
- Registered with
- Pakistan Software Export Board (G) Ltd.
- Government authority
- Ministry of Information Technology & Telecommunication, Government of Pakistan
- Registration type
- Company / Firm
- Valid from
- Valid till
- Renewed annually with PSEB.
Company registration
Woltrio LLC is the US legal entity behind Woltrio, registered in Colorado and listed with Dun & Bradstreet and Creditsafe. These are the identifiers a procurement or compliance team uses to check a vendor, so they are published here rather than sent on request.
Opens the Colorado Secretary of State business record for ID 20268285348, the public source for the entity's status and formation date.
- Legal name
- Woltrio LLC
- Entity type
- Limited liability company (LLC)
- Jurisdiction
- Colorado, United States
- Colorado Secretary of State ID
- 20268285348
- Incorporated
- Woltrio has operated since 2024; the Colorado LLC was formed in October 2026 as its US legal entity.
- Operating since
- 2024
- Headquarters
- 1500 N Grant St, Suite 5034, Denver, CO 80203, United States
- D-U-N-S number
- 14-961-5138Issued by Dun & Bradstreet. Look it up on dnb.com or use it in your vendor onboarding system.
- Creditsafe Safe Number
- US233901870Creditsafe reports are subscription-only; the Safe Number identifies Woltrio LLC in their database.
- NAICS code
- 541511 · Custom Computer Programming Services
- Business profiles
Compliance
The certification we hold, and the regulatory frameworks we build our clients' software to meet.
HIPAA
Health Insurance Portability and Accountability Act
- BAA signed before any PHI is shared
- PHI stays in your environment; we develop with synthetic data
- Encryption, access controls and audit logging built into your product
- Breach notice within 3 business days
GDPR
General Data Protection Regulation (EU)
- Data Processing Agreements (DPA) with SCCs
- Data subject rights procedures documented
- Privacy by design principles implemented
- Sub-processor transparency maintained
PIPEDA
Personal Information Protection and Electronic Documents Act (Canada)
- Consent-based data collection
- Individual access to personal information
- Safeguards for personal information
- Accountability for data protection
Security Controls
Controls certified to ISO/IEC 27001:2022 at our development center.
Information security for use of cloud services
Processes for acquisition, use, management and exit from cloud services shall be established in accordance with the organization's information security requirements.
Authentication information
Allocation and management of authentication information shall be controlled by a management process, including advising personnel on the appropriate handling of authentication information.
Remote working
Security measures shall be implemented when personnel are working remotely to protect information accessed, processed or stored outside the organization's premises.
Application security requirements
Information security requirements shall be identified, specified and approved when developing or acquiring applications.
Clock synchronization
The clocks of information processing systems used by the organization shall be synchronized to approved time sources.
Subprocessors
Services Woltrio uses to run its own business, each under its provider's data processing terms. None of them receives PHI.
Amazon Web Services (AWS)
Cloud infrastructure for Woltrio's own systems
United States (vendor HQ)
Anthropic
AI assistance for internal engineering work (API, no training on our data)
United States (vendor HQ)
Cloudinary
File and image storage for our website and internal tools
United States (vendor HQ)
GitHub
Source code hosting and version control
United States (vendor HQ)
Hostinger
Business email
Lithuania (vendor HQ)
Google Meet
Video meetings with clients
United States (vendor HQ)
Microsoft Teams
Video meetings with clients
United States (vendor HQ)
Zoom
Video meetings with clients
United States (vendor HQ)
FAQ
Common questions about our security and compliance practices.
Data storage and encryption
Where is my data stored?
Products we build for you run in your own cloud account; for healthcare clients, that is your AWS account, covered by your BAA with AWS. Woltrio does not host your production data or PHI on its own systems. Our own business systems (email, source code, file storage and meetings) use the subprocessors listed on this page.
How is data encrypted?
We follow our Cryptography & Key Management Policy: TLS 1.2 or higher for data in transit and AES-256 for data at rest, using the cloud provider's key management where available. Backups of sensitive data are encrypted the same way.
Does Woltrio store or see PHI?
No. PHI stays in your environment. We build and test with synthetic data only, and none of our subprocessors receives PHI. Because we hold no PHI, we have no vendor BAAs of our own; we sign a BAA directly with you.
How will I hear about changes to your subprocessors?
The subprocessor list on this page is kept up to date, and changes are also reflected in our Privacy Policy.
Access and records
How is access to my systems controlled?
Under our Access Control Policy, access follows least privilege and need-to-know. You grant our engineers named accounts in your environment with only the permissions the work needs, and you can review or revoke them at any time.
Can I see a record of your access to my systems?
Yes. Because we work through accounts you grant, our actions are recorded in audit logs in your own account, so you hold the record, not us.
What happens when our engagement ends?
We hand over source code, documentation and credentials, remove our access to your environments, and securely delete project data held on our own systems under our Data Retention & Secure Disposal Procedure, unless you ask us to keep it or a contract requires otherwise.
Compliance
Do you build GDPR-compliant software?
Yes. We design and build software to meet GDPR requirements — privacy by design, documented data subject rights workflows, data minimisation and sub-processor transparency in the systems we deliver. GDPR compliance is something your product achieves, not a certificate a vendor holds; Woltrio's independently certified standard is ISO/IEC 27001:2022, held by its development center. A Data Processing Agreement (DPA) with Standard Contractual Clauses (SCCs) is available upon request for projects where we process personal data on your behalf. Contact legal@woltrio.com.
Do you build HIPAA-compliant software?
Yes. We build healthcare software designed to meet HIPAA requirements, with encryption, access controls and audit logging built into your product. HIPAA compliance is something your organization and product achieve, not a certificate a vendor holds. As your business associate, we sign a BAA before any PHI is shared; our commitments are listed in the Healthcare and HIPAA section at the top of this page.
Will the FDA regulate our healthcare software?
It depends on what the software is intended to do. Scheduling, billing, patient portals and most EHR features are generally not medical devices. Software that diagnoses, monitors patients or recommends treatment can be regulated by the FDA as Software as a Medical Device (SaMD), and so can some clinical decision support tools. We don't make that call ourselves: if your product includes features like these, we flag them during scoping and recommend that a regulatory consultant decides. We then build to the requirements they set.
Is Woltrio ISO 27001 certified?
Yes. The information security management system at Woltrio's development center is certified to ISO/IEC 27001:2022 by G-CERTI, an IAS-accredited certification body (certificate no. GKPK-0328-IC, first issued 9 April 2026). The scope covers the design, development, deployment and provision of our software solutions, including healthcare software, AI systems, cloud solutions and API integrations. Our headquarters in Denver, Colorado is outside the certificate's scope. The certification is maintained through annual surveillance audits. You can view the certificate and its verification details in the ISO/IEC 27001:2022 section at the top of this page.
Is Woltrio registered with the Pakistan Software Export Board (PSEB)?
Yes. Woltrio is registered with the Pakistan Software Export Board (G) Ltd. under the Ministry of Information Technology & Telecommunication, Government of Pakistan, as a company/firm (registration no. Z-25-13327/25, valid February 2026 – January 2027, renewed annually). You can view the certificate and verify it on PSEB's portal in the PSEB registration section of this page.
Is Woltrio PCI compliant?
Woltrio is not itself a PCI DSS-assessed entity. Card payments are processed by Stripe, a PCI DSS Level 1 Service Provider, so cardholder data never touches Woltrio's servers. Software we build for clients is designed to keep card data inside the payment processor's scope in the same way.
Can I get a Business Associate Agreement (BAA)?
Yes. We sign our standard Business Associate Agreement before any PHI is shared, and you can review it before you sign a contract. It commits us to notify you of a breach within 3 business days. Contact legal@woltrio.com.
What certifications and compliance standards does Woltrio maintain?
Woltrio's development center holds ISO/IEC 27001:2022 certification (G-CERTI, certificate no. GKPK-0328-IC), maintained through annual surveillance audits. We do not have a SOC 2 report, and none is currently planned. We build client software to meet HIPAA and GDPR requirements and design systems that support your own SOC 2 audit.
AI and Data Usage
Is my data used to train AI models?
No. Woltrio uses Anthropic's API for internal engineering work such as code assistance, under Anthropic's commercial terms, which do not allow training on our data. It never receives PHI or your production data. We do not sell or share your data, or use it for anything other than the work you contracted.
What AI services does Woltrio use?
Anthropic (Claude), through its API, for internal engineering work. If that changes, the subprocessor list on this page is updated.
What about AI features you build into my product?
They run under your own agreements and accounts. In healthcare products, any PHI sent to an AI model stays inside your environment, for example a model accessed through your AWS account under your BAA with AWS. We send only the minimum data each feature needs.
Security and Incident Response
How does Woltrio handle security incidents?
We follow our Information Security Incident Response Procedure: identify, assess, contain, eradicate, recover and review. If an incident affects your PHI, we notify you within 3 business days of discovery, as our BAA commits, well inside HIPAA's 60-day limit. If it affects personal data under GDPR, we notify you without undue delay so you can meet the 72-hour deadline to your supervisory authority.
How can I report a security concern?
Email security@woltrio.com. Our Security & Privacy Officer, Ehtisham Ilyas, reviews every report.
How often are security audits performed?
Our development center's ISMS is audited every year by G-CERTI, and internally at least once a year under our Internal Audit Procedure. We scan for vulnerabilities under our Vulnerability & Patch Management Procedure. We do not commission our own penetration tests: clients usually commission an independent test before launch, and we support the testers and fix the findings.
What is Woltrio's uptime guarantee?
Uptime and recovery targets are agreed per project and written into your SLA. Your product runs in your own AWS account, and we design it for the availability your SLA requires.
Still have questions? Our team is here to help at security@woltrio.com
Questions about our security.
Our security team is here to help with audits, agreements, and anything else you need to move forward with confidence.
We reply the same business day, sign an NDA within 24 hours, and send a free scope within 3 business days. Nothing to pay upfront.